LDLC Confirms Data Breach: Customer Personal Information Accessed
French online retailer LDLC has reported a cybersecurity incident. Unauthorized access to one of its systems allowed cybercriminals to view customer personal data. This includes names, addresses, phone numbers, and account details. LDLC assures that banking information and passwords were not compromised.
The company is notifying affected customers via email. The exposed data includes first and last names, postal and email addresses, landline and mobile phone numbers, and potentially fax numbers if provided. User language preferences, individual or business account status, and "technical client codes"—internal LDLC identifiers—were also accessed.
Customer titles, such as "Doctor" or "Master," may have also been revealed, potentially indicating professions like doctors or lawyers. Account creation dates and last login dates were also part of the accessed information, offering insight into customer tenure and site engagement. Such details are valuable for fraudsters aiming to craft convincing phishing attempts.
LDLC states that bank account details (RIB), credit card numbers, login credentials, and passwords remained secure. The company has isolated the affected system, reviewed its access protocols, and notified the French data protection authority, CNIL.
As LDLC acknowledges, the primary risk from data leaks often emerges later. Fraudsters can use the collected personal information to create fake communications—like messages about blocked parcels or pending refunds—that appear legitimate by addressing the recipient by name, referencing their customer history, and using their real phone number. This is the core mechanism of phishing: impersonating a trusted entity to extract sensitive information.
LDLC emphasizes that its teams will never request passwords, banking details, or changes to bank information via email, SMS, or phone. Customers are advised to verify sender identities and link destinations before clicking on any communication. For suspicious calls, customers should not proceed and should instead contact LDLC through its official channels. Guidance on identifying malicious messages is available on the public website Cybermalveillance.gouv.fr. Business customers, whose status was among the exposed data, should be particularly vigilant regarding any requests for bank modification.
The company has not disclosed the number of affected customers, the date of the intrusion, or the method used by the attackers. It remains unclear whether the data was merely viewed or fully copied, and there is no confirmation of a complete database extraction. This incident echoes past security issues for LDLC, including a ransomware attack in late 2021 and previous customer data leaks in early and December 2024.
Fresh materials — Tech News
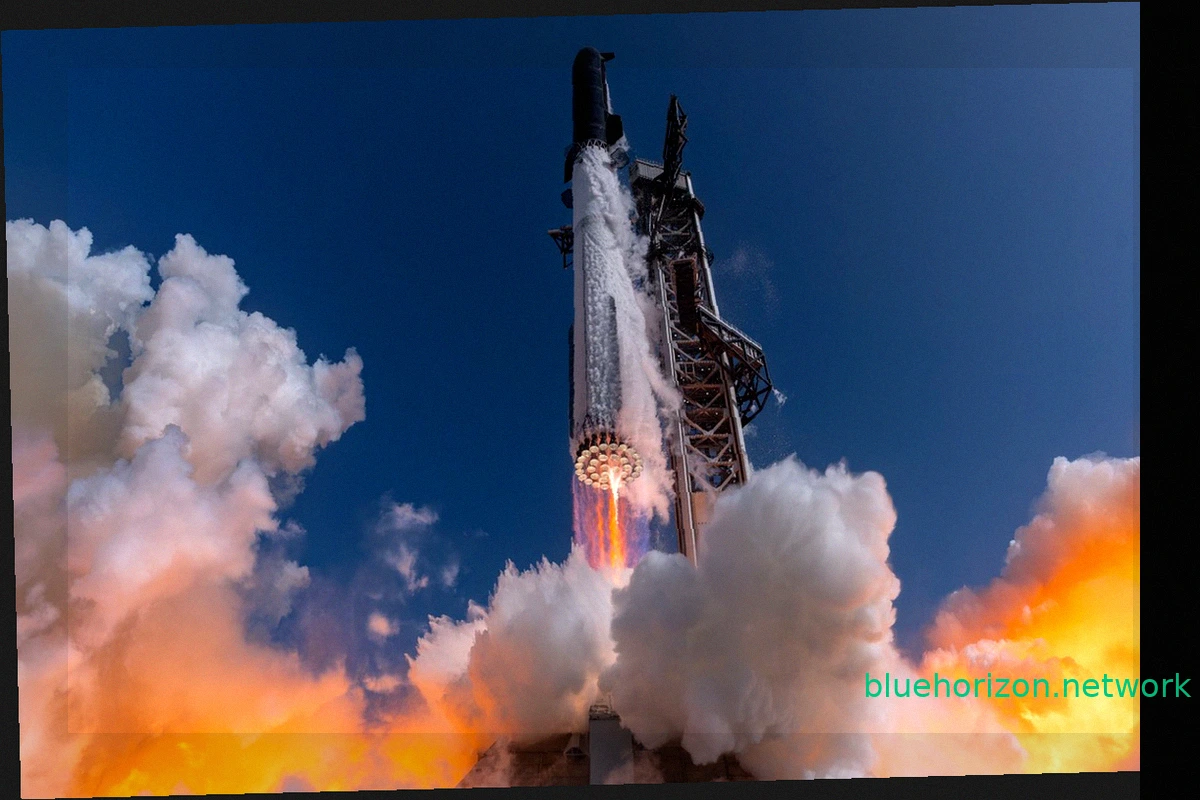
Google: Space Data Centers Need 1,800 Starship Launches
Google is developing orbital data centers. To make this project viable, the tech giant is awaiting significant progress from SpaceX and its Starship rocket. On October 1st, Google sent its first space-bound data center into orbit aboard a SpaceX Falcon 9 rocket. This mission wi
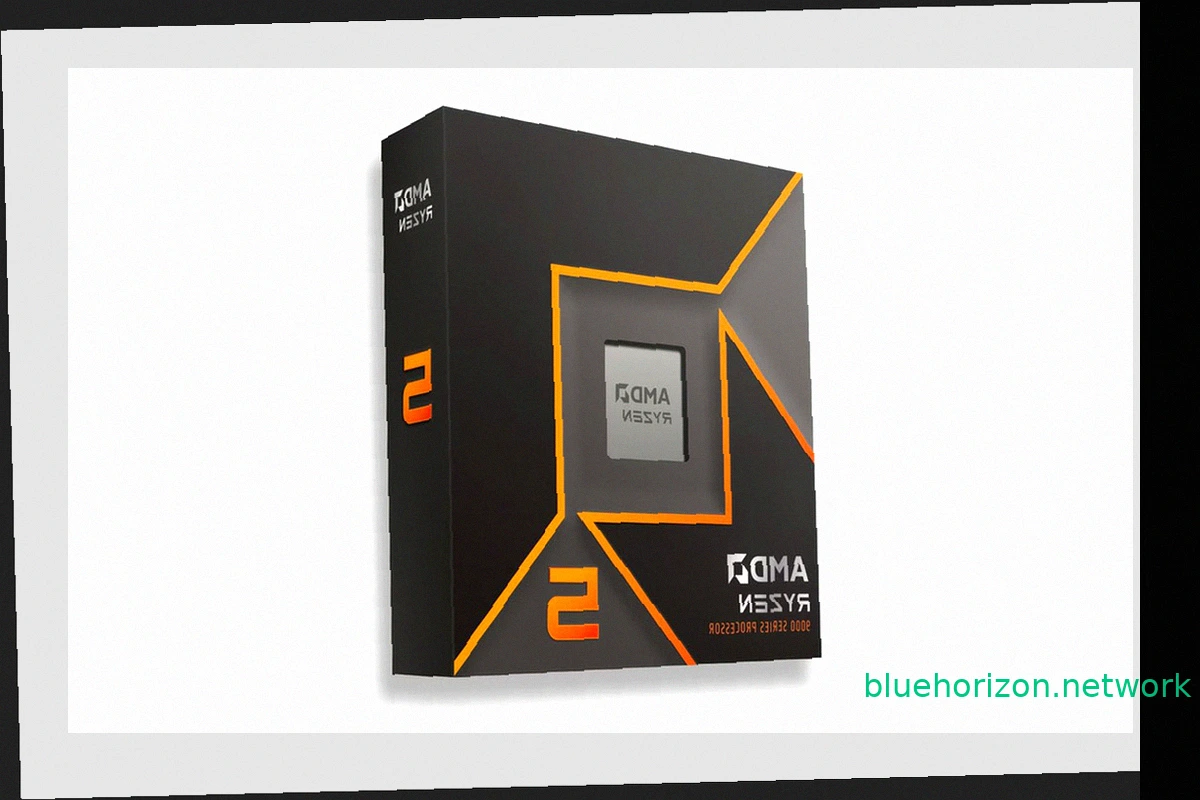
Ryzen 5 9600X Hits €142.36 on AliExpress for AM5 Builds
Our review highlighted the Ryzen 5 9600X not just for its raw performance, but for its remarkable efficiency and cool operation under load. Now, with a price cut to less than half its launch cost during AliExpress's Local Day, it presents a much more compelling option for an AM5 platfo
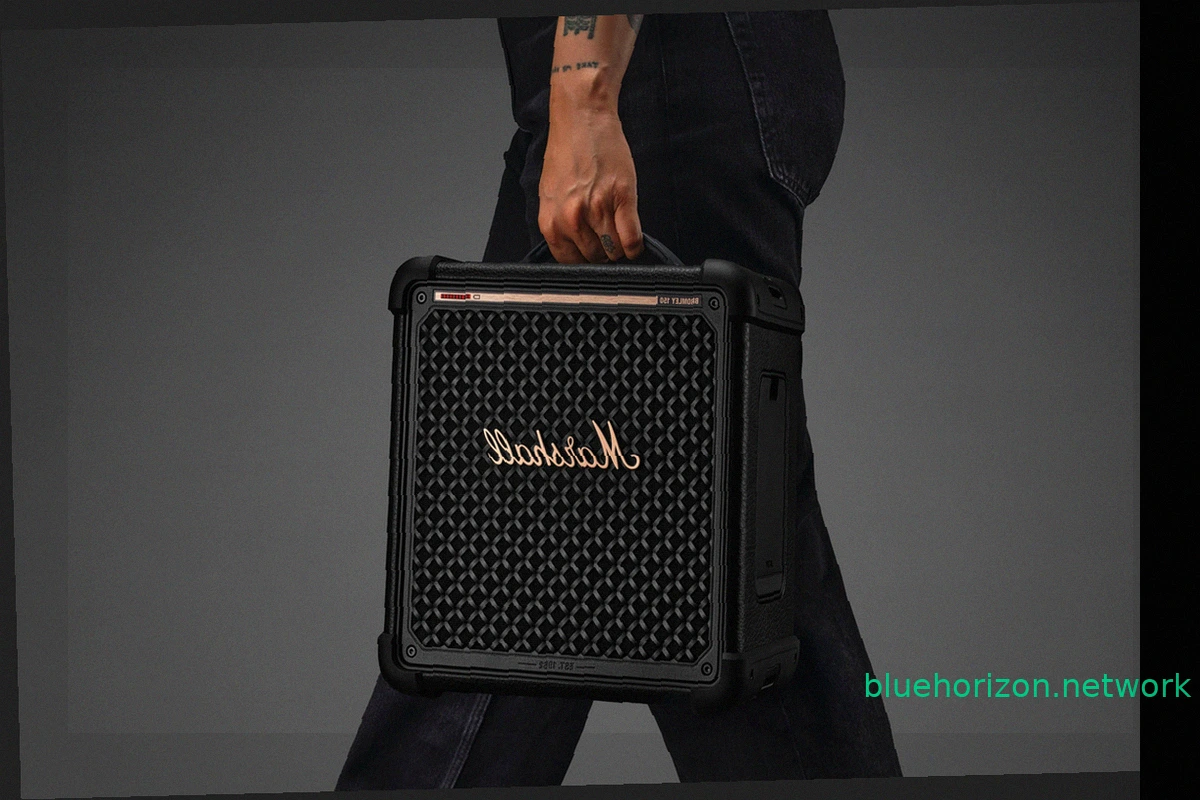
Marshall Bromley 150: Compact Speaker with Lights and Karaoke Features
The Marshall Bromley 150, a more compact party speaker, now includes music-synced lights. It retains two inputs for microphones or instruments and a removable battery offering around 40 hours of playback. The controls have moved to the left side to maximize the front panel for light effects, wh
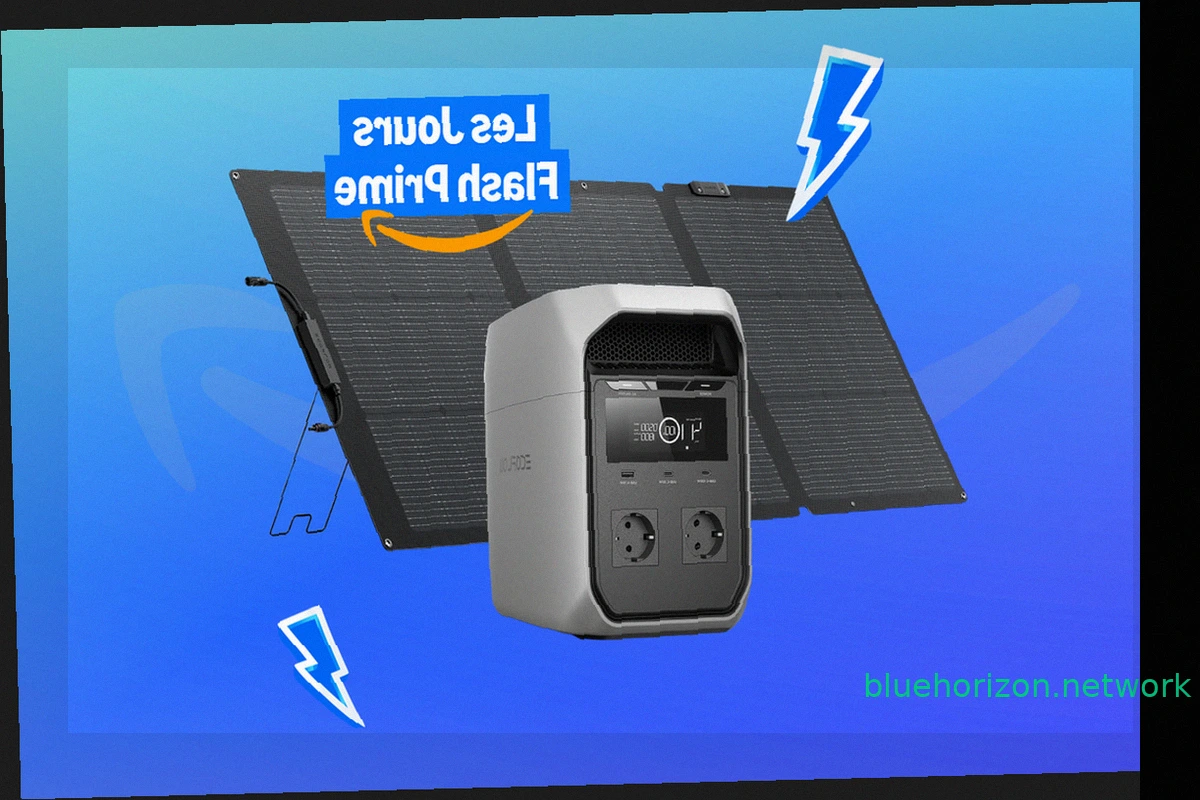
Ecoflow Delta 3 Classic: 130€ Off Before Prime Day
The Ecoflow Delta 3 Classic stands out for its compact design and, more importantly, its versatility. It can simultaneously charge an electric car and a smartphone, all at a 15% reduced price on Amazon. Get the Ecoflow Delta 3 Classic for 718 euros instead of 848 euros at Amazon. To tak
Saily's Unlimited eSIM for the US Drops to €36.89 Before the All Saints' Day Holidays
Saily, the travel eSIM from Nord Security (the company behind NordVPN), sells data plans by destination via its website or app. For the United States, their unlimited plan is priced daily for 1 to 30 days. The 15-day version currently costs €40.99. Using the code CLUBIC offers a 10% discoun
Piratage DGFiP: ANSSI reveals how stolen passwords led to catastrophe
ANSSI has released its incident report on the recent DGFiP hack. Stolen agent credentials, absent two-factor authentication, and unnoticed data exfiltrations are detailed in the document, explaining how the data of hundreds of thousands of users was leaked this summer. To